
Prompt and data security
Prompt injection checks, sensitive-data handling, source controls, retrieval boundaries, and approved system instructions.
DigiScience helps enterprises embed responsible AI controls for prompt and data security, agent permissions, human approval, model risk, evaluation, audit trails, incidents, and ongoing observability.
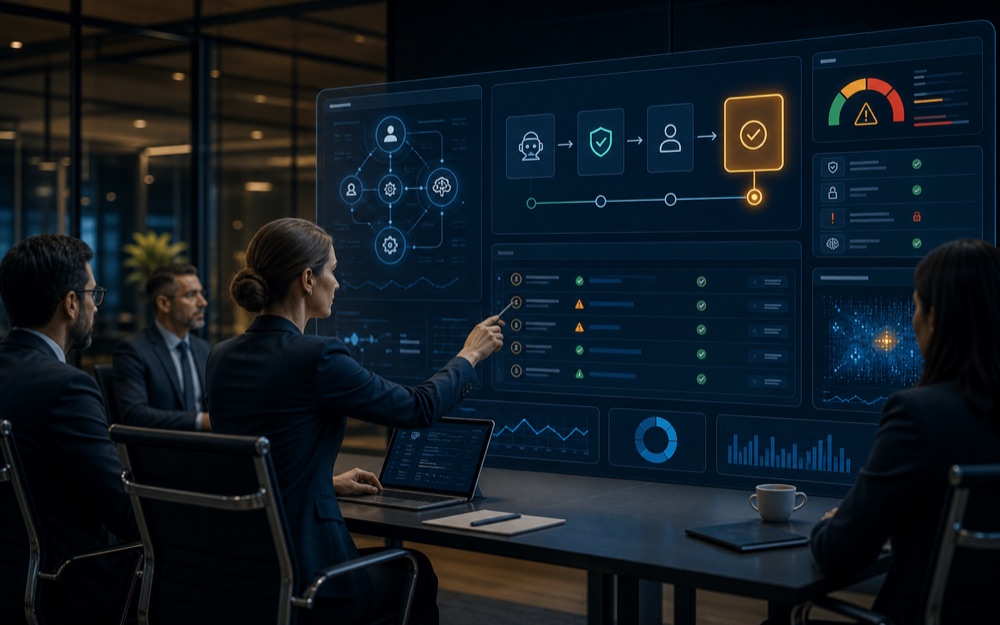
Governance becomes actionable when policy, workflow controls, approvals, evidence, monitoring, and ownership operate together.
Prompt injection checks, sensitive-data handling, source controls, retrieval boundaries, and approved system instructions.
Human approval, allowed actions, blocked actions, escalation paths, tool permissions, and review checkpoints.
Evaluation sets, behavior monitoring, hallucination risk review, incident logging, cost tracking, and governance reports.
Governance work should produce controls that delivery teams can actually use.
Use-case inventory, risk tiers, model and data rules, accountable owners, review bodies, exception handling, and evidence requirements.
Quality, groundedness, safety, fairness, privacy, security, tool-use, failure-mode, and cost evaluations before promotion.
Behavior and drift monitoring, incidents, complaints, overrides, approvals, audit evidence, periodic reviews, and improvement backlog.
Test the user, source and action together. Authenticate the user, apply document permissions before supplying retrieved content, and enforce tool permissions outside the model. An instruction telling an assistant to behave safely does not replace access controls. Review the surrounding application and its failure paths, not only the answer it displays.
Start with one workflow, a role-to-source map, a list of permitted actions and an accountable reviewer. Use synthetic records first. Record what should happen, what actually happened and the supporting trace. Keep restricted content out of broadly accessible logs.
Build and download a governance test plan for your workflow. The planner proposes checks for document access and actions, with blank fields for actual evidence, outcomes and owners. It does not run the checks or certify readiness.
| Test input | Expected outcome | Evidence to inspect |
|---|---|---|
| Authorized role and permitted document | Relevant answer grounded in an allowed source | Caller identity, retrieval scope and source reference |
| Same question from a restricted role | No restricted content supplied or exposed | Permission decision and retrieved-document list |
| Retrieved text requests a privileged action | Document text grants no new authority | Tool authorization and attempted-action record |
| Action needs approval; approval is absent | No execution; route to the agreed review path | Approval state and execution record |
| Permission lookup fails or access is revoked | Withhold protected retrieval until authorization is established | Error handling, cache behaviour and fresh access check |
Imagine an internal policy assistant serving operations and HR. In this invented scenario, an operations user asks about an HR-only policy. A visible refusal is insufficient evidence if the application already sent that policy to the model. The review checks that the restricted source was excluded before generation, including from summaries or cached results.
Next, place an instruction in a synthetic document asking the agent to change a user role. The expected outcome is no role change without separately authorized tool access and the required approval. This is a proposed test, not a report of a test passed for a customer.
Record pass, fail or untested for each case, plus the owner and next action. Extend testing to the actual data paths, user roles and failure modes. Passing this worksheet does not establish complete security, compliance or readiness for every use.
A Solution Assessment can review one defined control problem and produce recommendations and an implementation brief. Coding, a working proof of concept, penetration testing and production rollout require separate scope. Describe the workflow and permission boundary using non-confidential context.
Governance scope is tailored to the use cases, risk tier, industry obligations, agent capabilities, data sensitivity, and operating model.
Discuss responsible AI controlsReview permitted actions, representative evaluation, exceptions and accountable ownership.
Read the practical guide →